What is Northplane?
Headscale is a self-hosted implementation of the Tailscale control server: it lets Tailscale clients form a private network without Tailscale's servers. It doesn't come with a web interface, and Northplane is one, modeled on Tailscale's admin console.
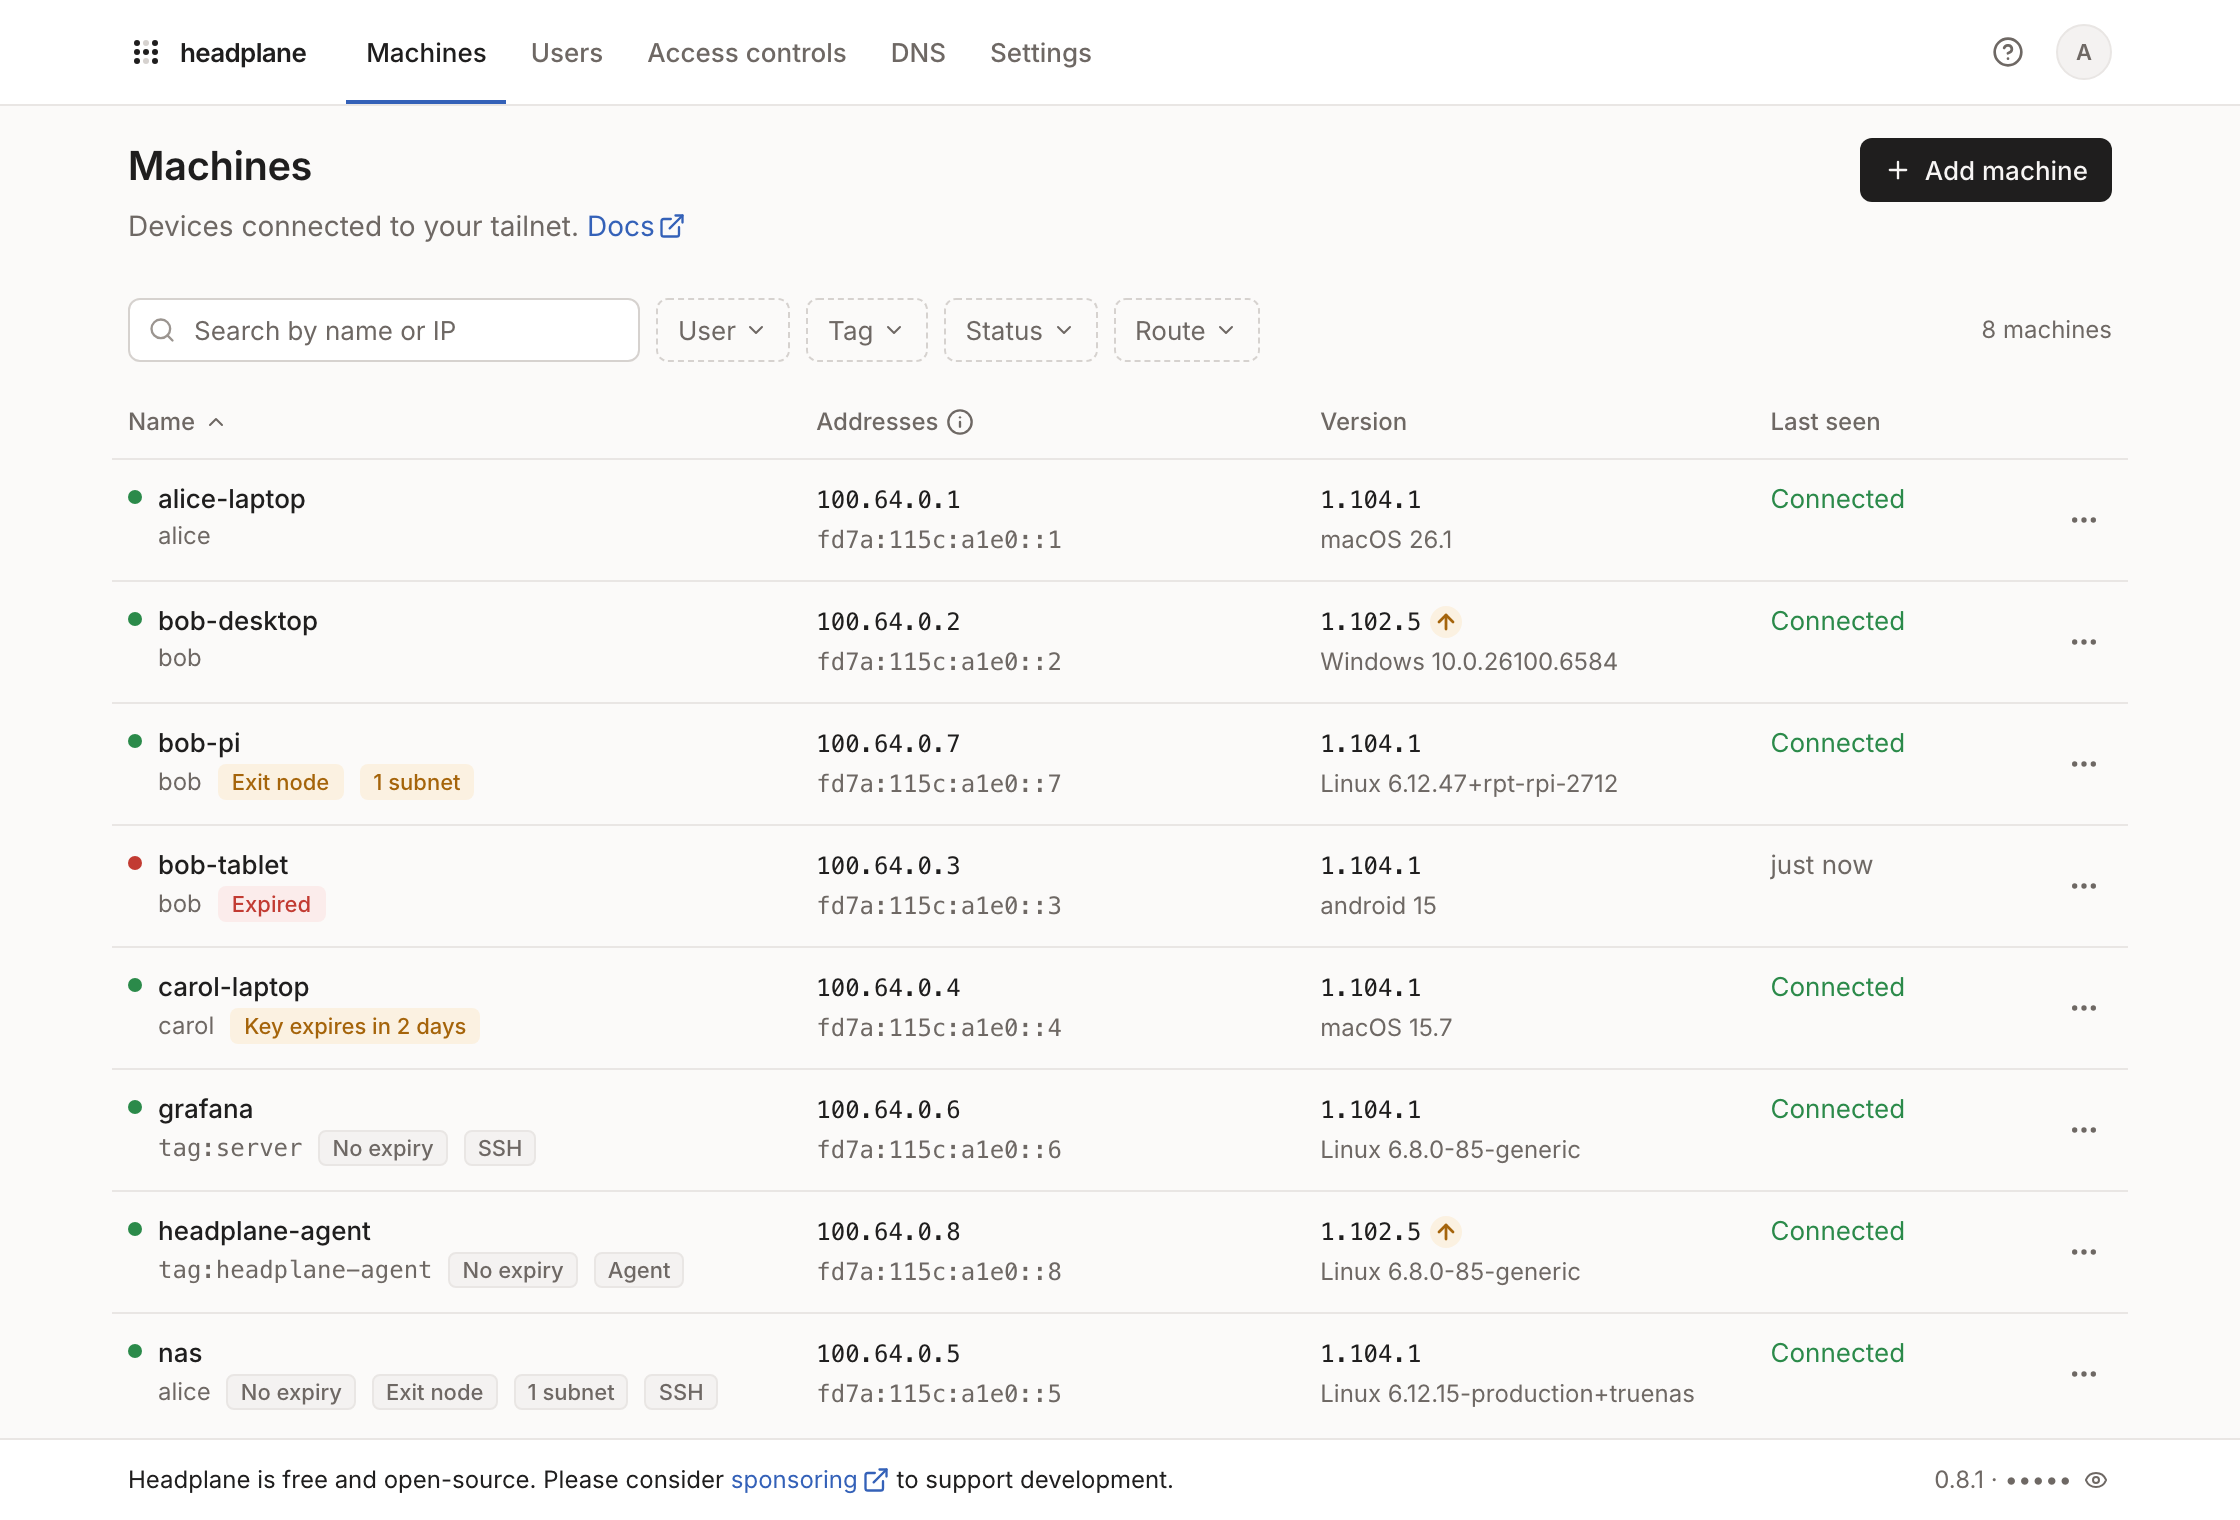
Northplane manages:
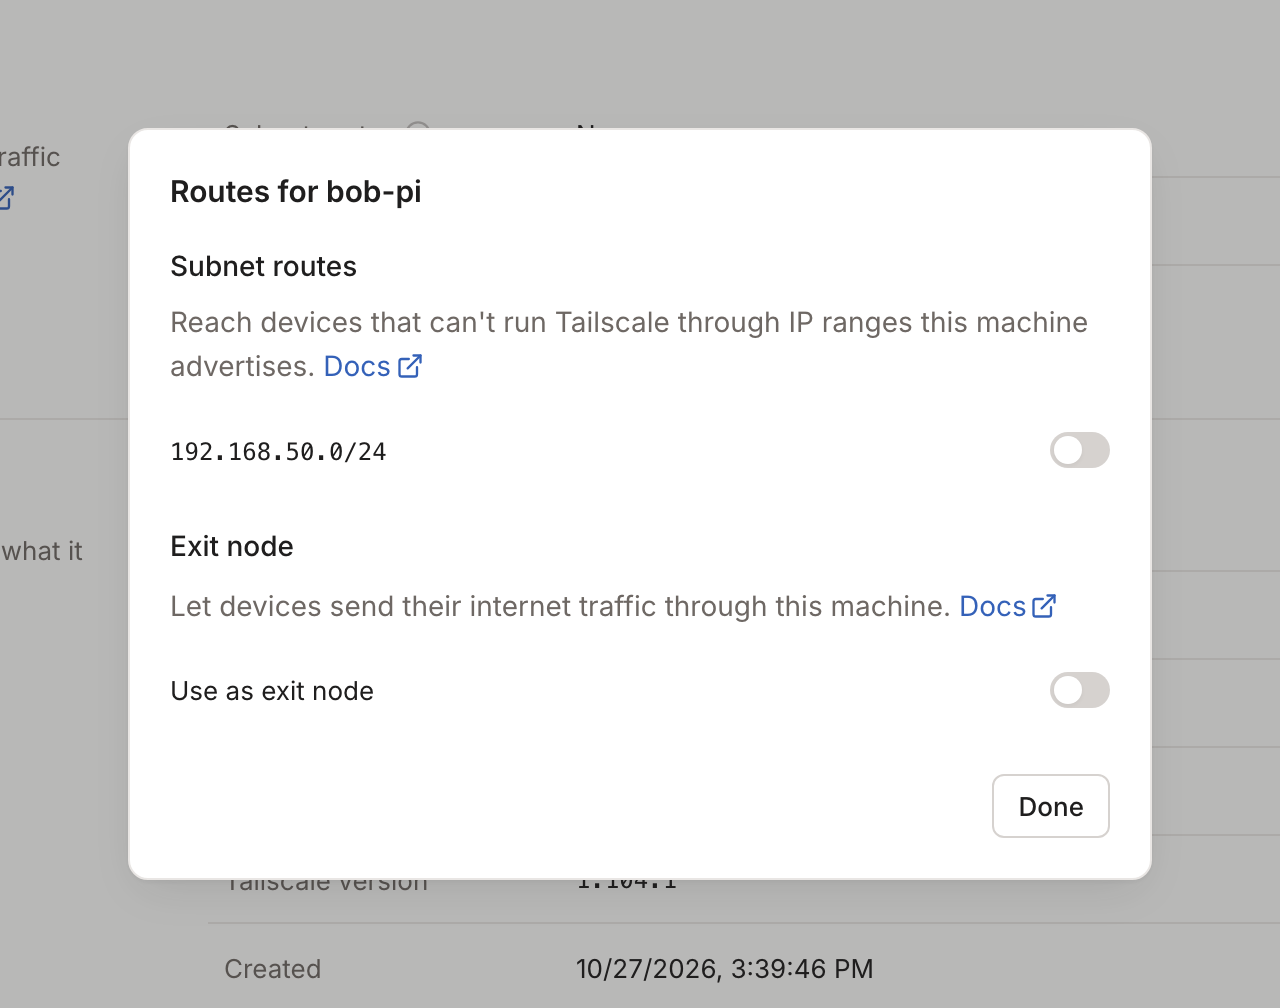
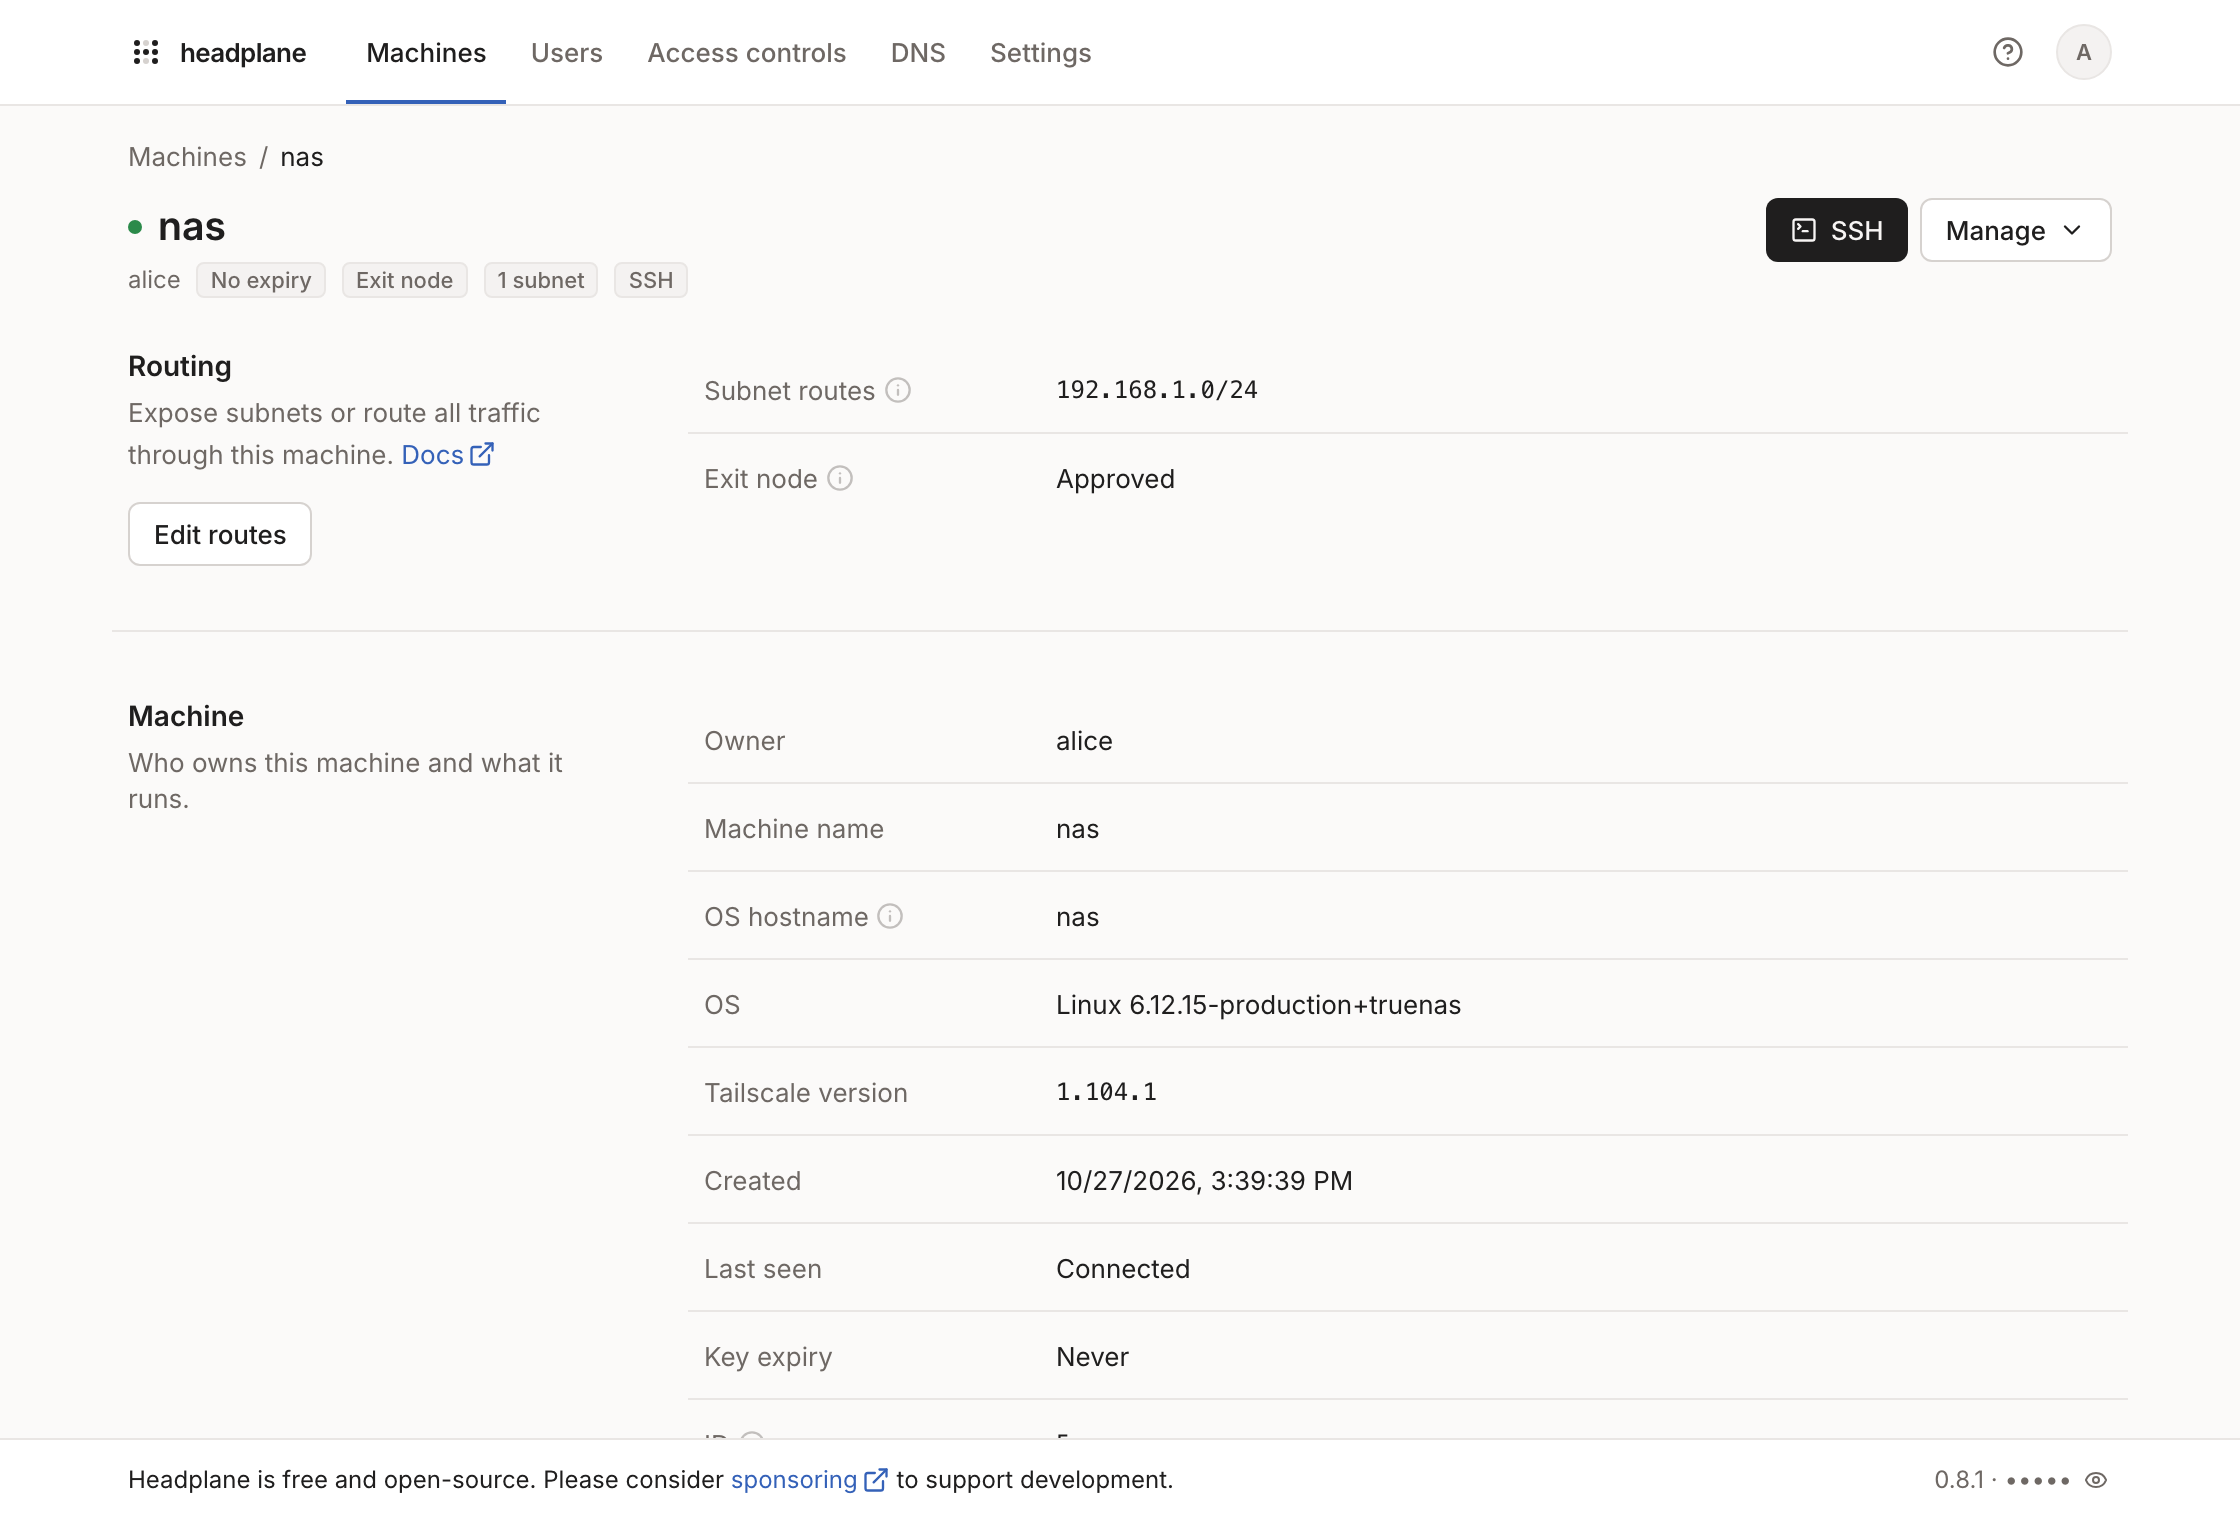
- Machines: rename them, change their owner, approve routes and exit nodes, manage tags, and expire or remove them
- Users and auth keys, including what each person can do in Northplane
- Access control: edit the ACL policy visually or as a file
- DNS: the tailnet name, Magic DNS, nameservers, search domains and records
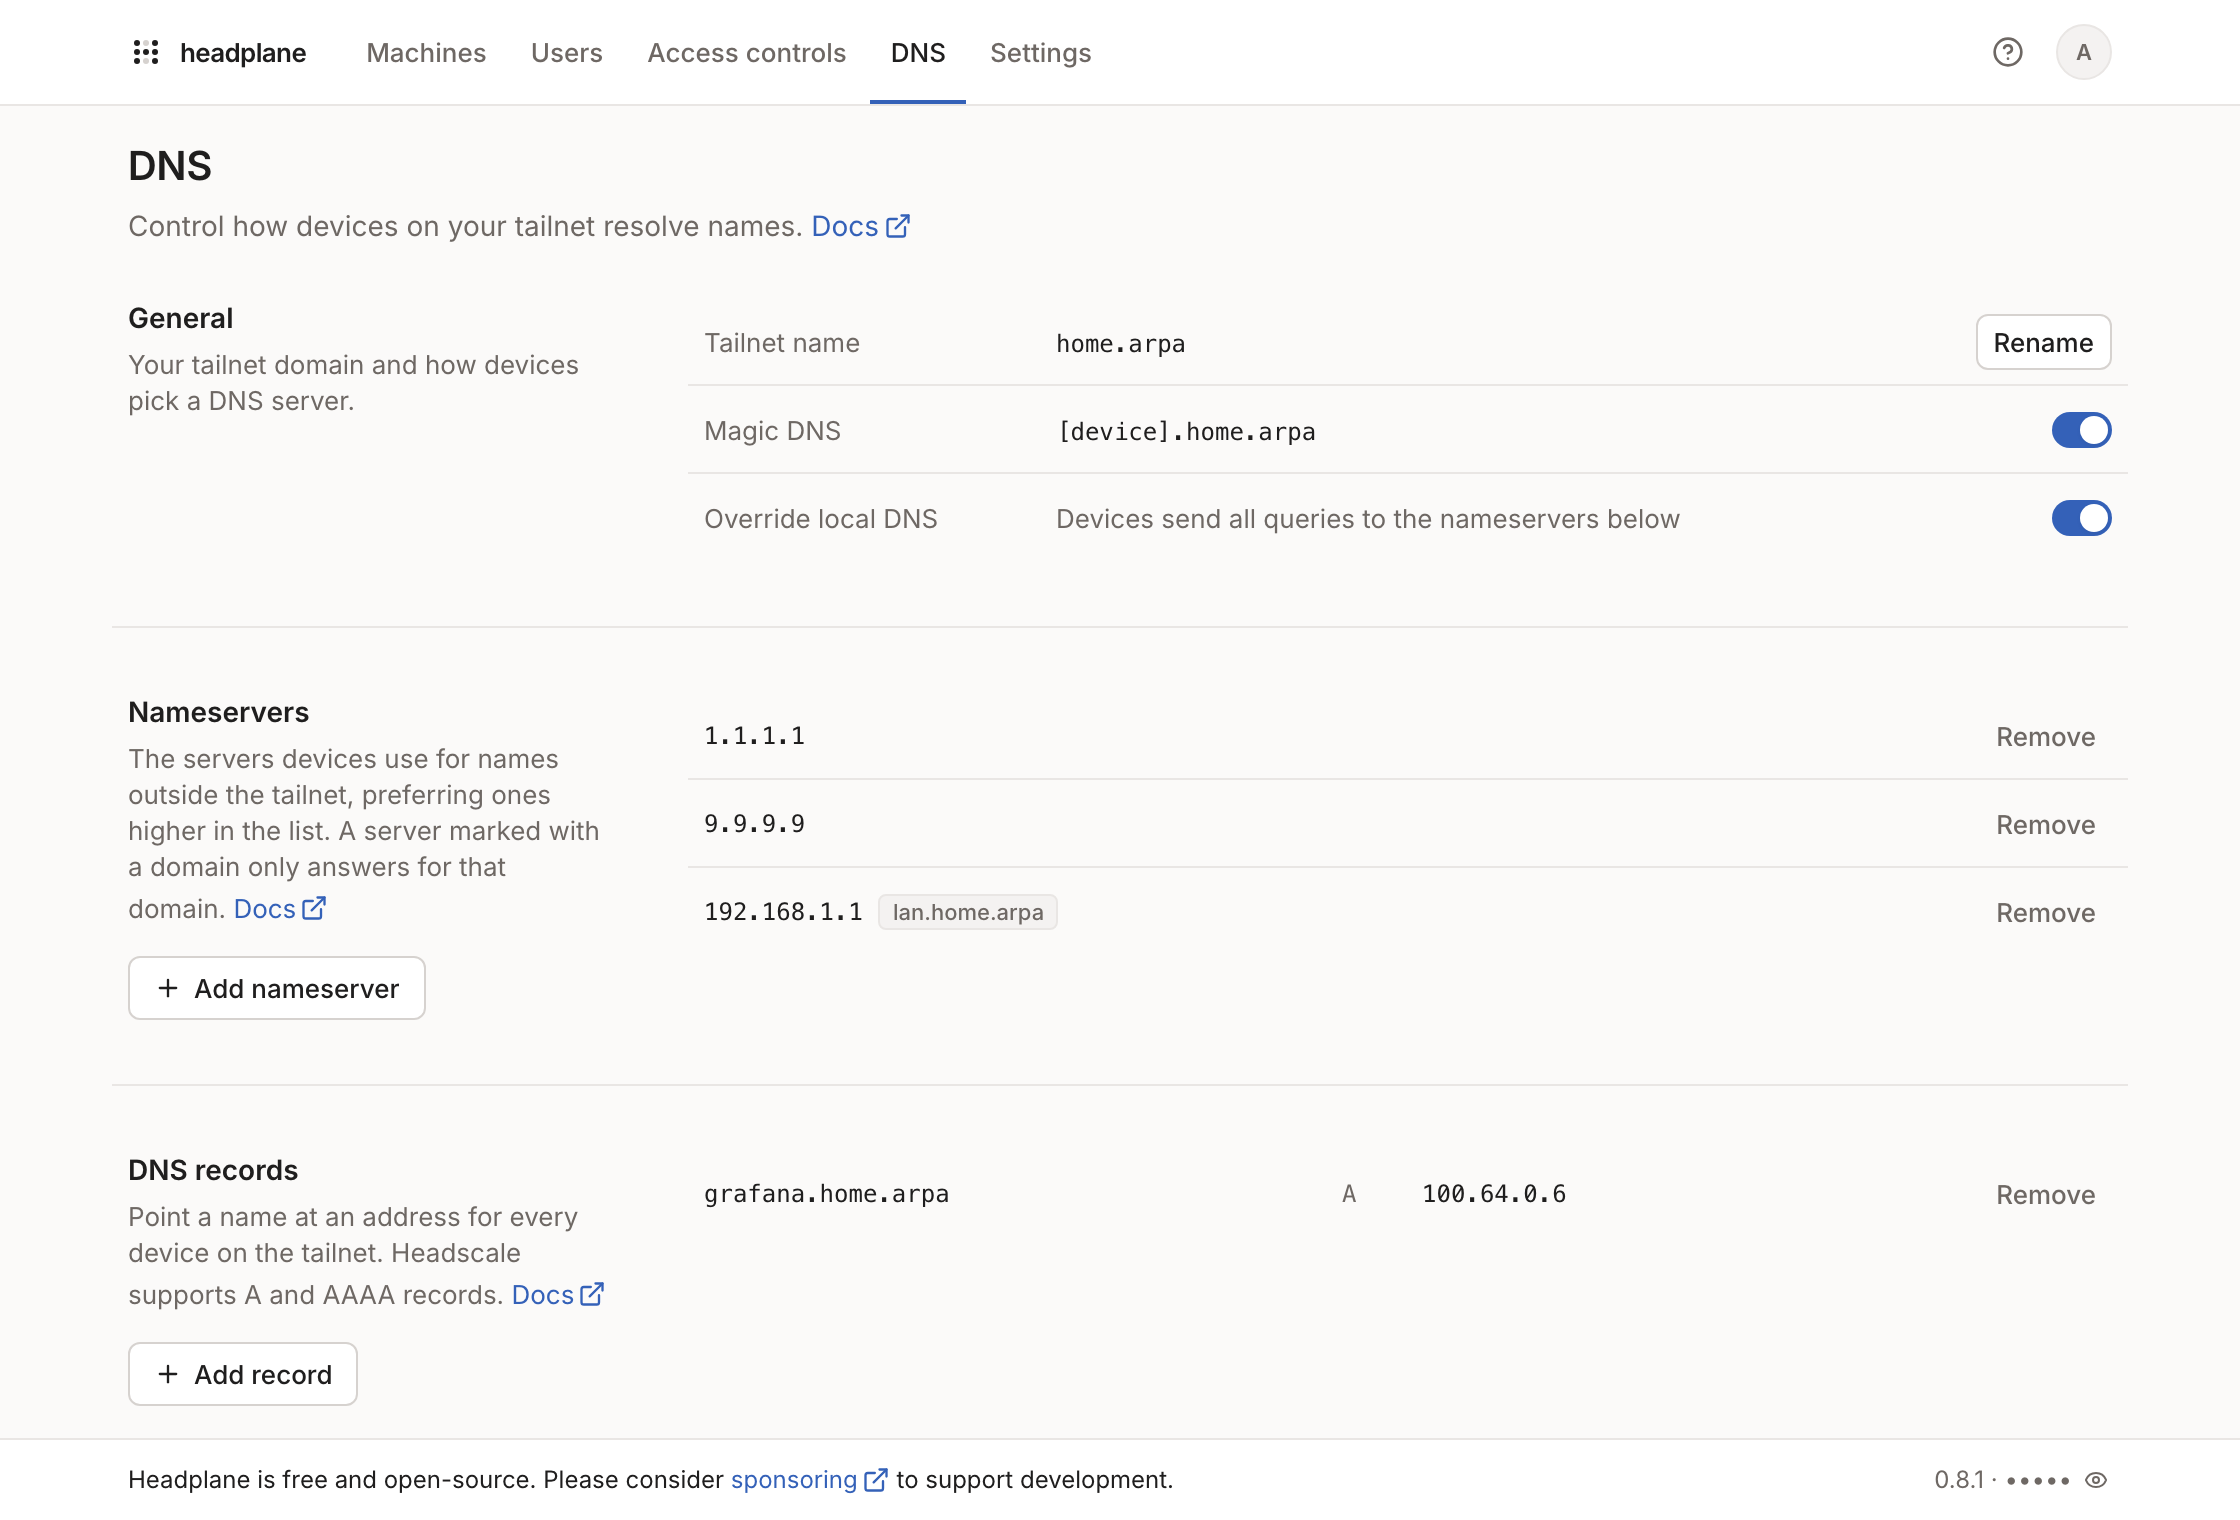
It also adds features Headscale doesn't have:
- Single sign-on through any OpenID Connect provider, or through a reverse proxy, with roles for each person
- Browser SSH into any machine on the tailnet, with no client installed
- The Northplane Agent, which shows each machine's Tailscale version, OS and connectivity
How it connects
Northplane is a separate server that runs next to Headscale. It reaches Headscale three ways, and each one unlocks part of the UI:
Northplane
- API keyRequiredHeadscale's APIMachines, users, auth keys and ACLs
- Shared fileOptionalHeadscale's config fileDNS and sign-in restrictions
- AgentOptionalThe tailnetMachine versions and Browser SSH
Only the API is required. Access to Headscale's config file is covered under Integrations, and the agent has its own page.
To get started, follow the Quickstart for a new server, or Installation to add Northplane to an existing Headscale.